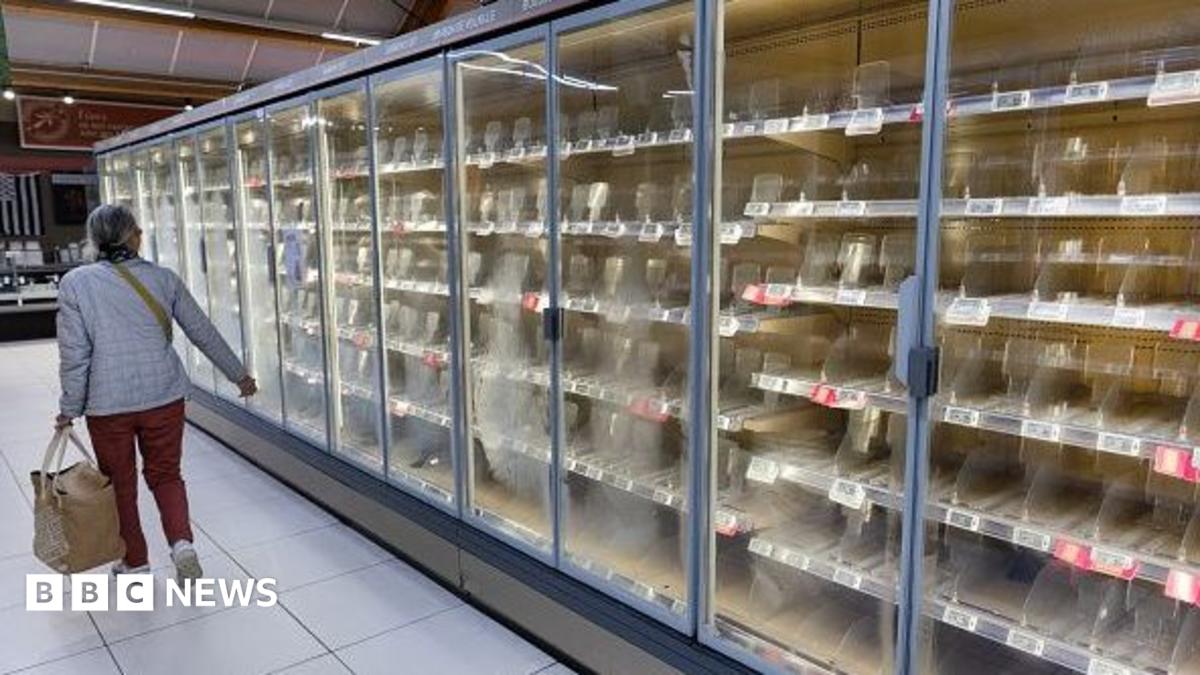

Supermarkets across Europe have recently experienced disruptions due to a possible cyber-attack that affected their refrigeration systems. This incident has raised alarm bells regarding the security of internet-connected devices, which range from industrial machinery to everyday appliances.
Internet-enabled devices, such as fridges, heating systems, and washing machines, offer increased remote control capabilities. However, any device that connects online can also be susceptible to exploitation by cybercriminals.
Although the risk is present, it does not imply that hackers can easily gain control over these systems. Major brands typically implement significant security measures to protect their technologies.
Previous vulnerabilities have been identified in various devices; for instance, in 2015, researchers showcased how a flaw in a Samsung smart fridge allowed for the interception of internet traffic.
Nevertheless, there is currently no evidence indicating that domestic appliances were targeted in the recent attacks on supermarkets during November.
Ciaran Martin, the former chief executive of the UK’s National Cyber Security Centre (NCSC), emphasized that manufacturers must take greater responsibility for ensuring the security of connected devices. “We need to demand more from big tech to provide us with safer products,” he stated.
He further recommended that consumers regularly update their devices and enable multi-factor authentication when available. “While it might be inconvenient, it only requires a few seconds,” he added.
Since April 2024, UK legislation mandates that manufacturers of specific consumer smart devices adhere to minimum cybersecurity standards, including protocols around password strength and regular security updates.
The NCSC is actively working with international partners to comprehend the supermarket incidents. As of now, they report no impact on the UK market.
However, findings from researchers at UK Cyber Defence have revealed over 800 interfaces related to refrigeration and building controls linked to British retailers, which can be accessed publicly on the internet.
While this does not automatically imply these systems are vulnerable to hacking, it does indicate a risk of exposure from weak passwords or software flaws.
In light of prior cyber incidents, the government has already initiated discussions with key food retailers to bolster their cyber resilience.
Helen Dickinson, chief executive of the British Retail Consortium, expressed that cyber incidents pose a significant concern for retailers, with many collaborating with the NCSC to exchange intelligence and enhance their security measures.
This is not the first scenario where cyberattacks have raised concerns about their potential effects on the food supply. In May 2025, when the UK supermarkets M&S and Co-op fell victim to ransomware attacks, customers faced empty shelves due to disruptions in fresh deliveries.
According to Tom Hegel, a researcher at the cybersecurity firm SentinelOne, clarity on security ownership is essential for retailers. “They need to define who is responsible for securing that equipment, not just maintaining it,” Hegel commented.
He noted that while internet connectivity enhances the convenience of daily technology, security should evolve in tandem. “Once attackers can manipulate those controls, operations like defrosting can be weaponized for disruption,” Hegel warned. Altering a simple setting can destroy physical stock, not just interfere with digital systems.
Editor’s Take
This development underscores the urgent need for improved cybersecurity measures across all sectors, especially in the retail industry reliant on connected devices. As threats evolve, brands and consumers alike must prioritize security to safeguard essential services. Enhanced regulations and awareness are critical to preventing disruptions that could significantly impact food supply chains and consumer trust.
Source: www.bbc.co.uk