
Massive Security Breach Exposes Vulnerabilities in Refrigeration Controllers
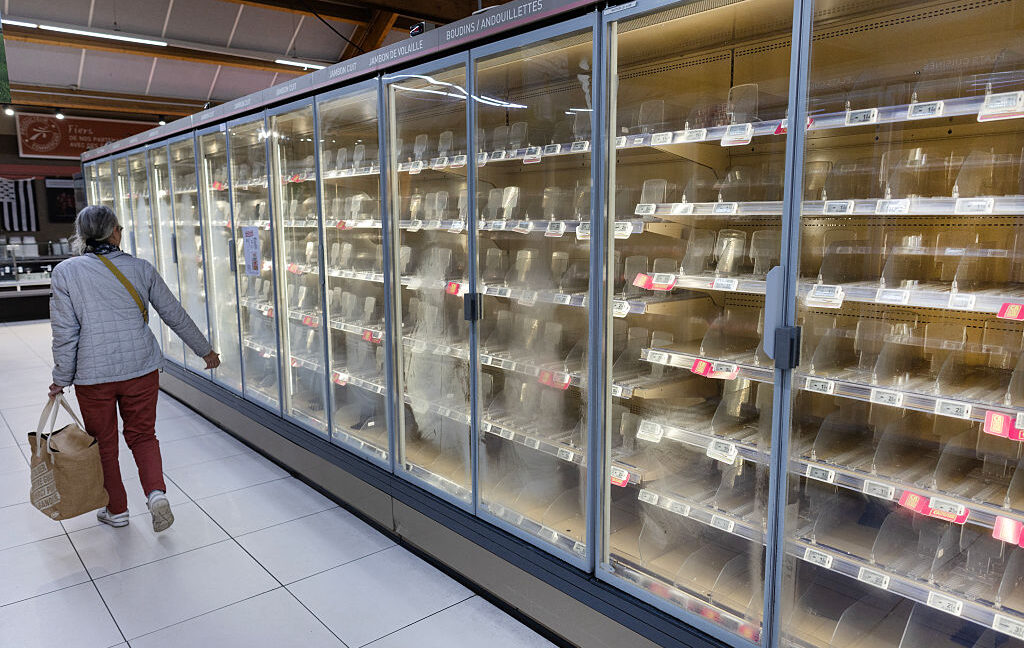
A significant cyber attack recently compromised supermarket systems across several European countries, reportedly costing businesses tens of millions of euros. The hack targeted refrigeration controllers that were not equipped with updated firmware and were inadequately secured, lacking basic protective measures like VPNs and IP whitelisting.
Security researchers from Pen Test Partners highlighted two primary factors that could have mitigated this issue. In a statement, they emphasized the importance of implementing “cyber hygiene” practices. This includes removing the controllers from public internet access, utilizing VPNs for remote connections, managing third-party devices within a secured network, updating default passwords, and ensuring systems are regularly patched to the latest versions.
Concerns regarding the security of these controllers were previously voiced by Claroty last October, along with a similar warning from the U.S. Cybersecurity and Infrastructure Security Agency (CISA) in February. Both organizations stressed the potential dangers of neglecting basic cybersecurity protocols in industrial contexts.
In response to the attack, Copeland, the manufacturer of the affected controllers, acknowledged a vulnerability in an outdated model and stated that they are collaborating with clients to prevent future occurrences. However, representatives from Danfoss, which has been implicated in this breach, did not provide immediate comments regarding the situation.
As for the perpetrators of the attack, their identity remains unknown. This silence leads to speculation regarding their motivations—ranging from potential vandalism to the possibility of state-sponsored disruptions aimed at causing widespread chaos across Europe.
This incident raises important questions about the balancing act between the financial interests and security needs of companies. Often, organizations hesitate to invest significantly in cybersecurity until they experience severe consequences, such as a massive breach. The impacted supermarket chains are likely to face tough decisions moving forward, but it remains uncertain whether this cautionary tale will influence other businesses to prioritize cybersecurity investments.
Editor’s Take
This cybersecurity breach serves as a stark reminder of the vulnerabilities present in industrial systems, particularly in an era where digital connectivity is paramount. Businesses must recognize that investing in robust security measures is not merely a cost but an essential strategy for risk management. The consequences of neglecting such investments can be devastating, not only for individual companies but also for broader supply chains and consumer trust.
Source: arstechnica.com