Russian Hacktivists Claim Responsibility for Freezer Hacks Amid Ongoing Speculation

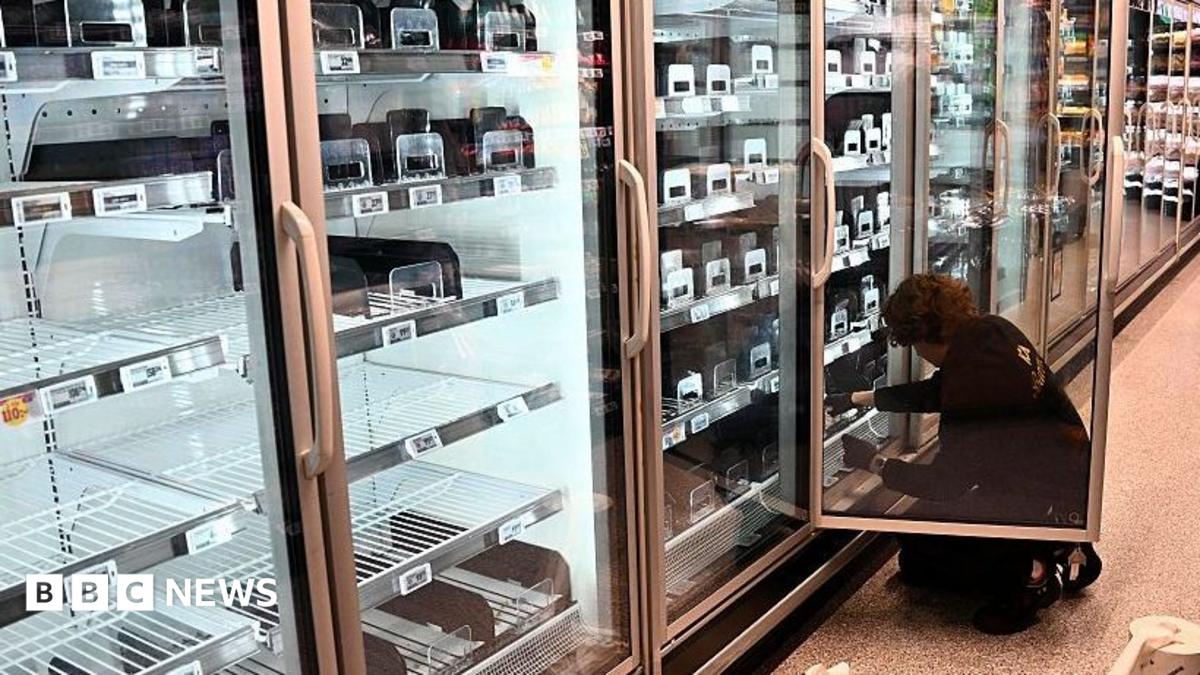
Two Russian hacktivist groups have announced their collaboration on the recent wave of hacks targeting freezer systems in European supermarkets. The groups, known as Noname057(16) and Z-Pentest Alliance, took to Telegram to claim responsibility, asserting they have once again displayed their “high level of skill and precision” in executing such attacks.
However, skepticism surrounds their claims as their posts and channels have since been removed. Cybersecurity experts are investigating evidence collected from so-called “honeypots” to uncover the true perpetrators behind these freezer hacks.
While Russian hackers remain a primary suspect, industry experts have not ruled out the involvement of Iranian hacktivists, sophisticated state-sponsored hackers, or even pranksters. Three separate cybersecurity firms have set up deceptive freezer software traps, allowing them to observe how hackers exploit these systems.
A “honeypot” serves as a digital decoy—like a fake network or file—designed to attract malicious actors. By analyzing these traps, cybersecurity professionals can study attack strategies without jeopardizing real systems.
Evidence from the initial cyberattacks indicates that the subsequent wave was notably targeted. According to Ryan Dewhurst from the Spanish cybersecurity firm Previdian, the simultaneous attacks on multiple freezer systems hint at thorough planning and coordination.
The vulnerabilities that were exploited in the affected freezer software were not particularly challenging to access due to their weak security and the availability of known attack methods online. However, experts like Dewhurst point out that the hackers had to compile information on the devices’ public IP addresses to create a targeted list, indicating a degree of meticulous planning and execution.
The timing of the temperature modifications—reportedly occurring overnight to maximize damage—further reinforces the idea of a well-coordinated effort behind the attacks.
Another firm, Lupovis, also engaged in using similar honeypot technology to gain insight into hacker tactics. Its honeypots appeared as if located globally, but activity surged just ten days before the second wave of attacks commenced.
Interestingly, the Lupovis team observed that hacking attempts were confined mainly to Europe, with no activity recorded against honeypots in regions like Africa or South America. Even their honeypots in Ukraine remained untouched.
Editor’s Take
The collaboration between these hacktivist groups highlights a growing trend in cyberattacks where coordination enhances the impact on critical infrastructure. This not only poses significant risks to businesses but also raises alarms for consumers reliant on these services, emphasizing the urgent need for improved cybersecurity measures. Understanding these attacks is vital for developers aiming to strengthen system defenses in an increasingly connected world.
Source: www.bbc.co.uk