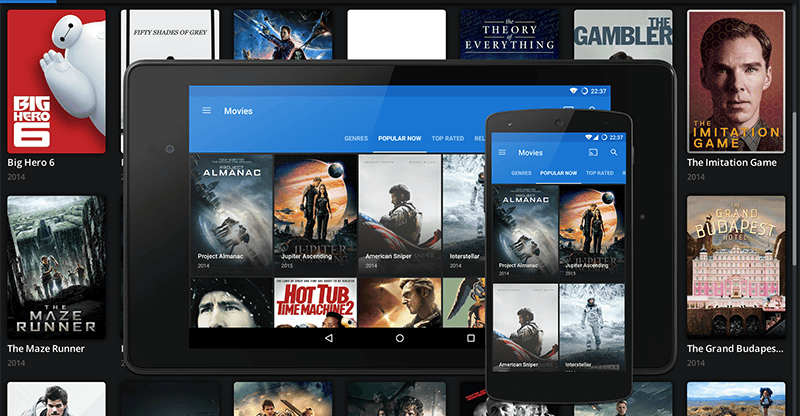

Popcorn Time, the controversial app once heralded as the “Netflix of Piracy,” has not been actively developed for years. Nevertheless, remnants of its legacy remain, with millions of users unknowingly kept at risk. Recent research from Eye Security has revealed that the updater for a particular Popcorn Time fork, known as “Time4Popcorn,” is still operational on numerous Windows, macOS, and Android devices globally. This updater continues to connect to defunct web domains using unencrypted HTTP and runs an outdated, vulnerable version of Chrome.
According to Niels Teusink from Eye Security, this updater could potentially install and execute any type of software with full system privileges. This vulnerability presents opportunities for malicious actors to construct a botnet simply by compromising one of the associated domains, conducting man-in-the-middle attacks, or monitoring machines that run the outdated software.
To mitigate this threat, Eye Security took a proactive approach by registering one of the compromised domains. They dispatched a modified update that instructed the updater to disable itself. Despite the ethical implications of this intervention, the team emphasized that inaction would have posed greater risks to users. As stated, “The update process wasn’t doing anything functional anyway, it was only creating risk for users.”
The implications of their action varied by operating system. On Windows, the update effectively halted the updater using the Service Control Manager, without removing any files. For macOS, a shell script was utilized to prevent the updater from commencing. However, the researchers did not address the update for Android devices, where user consent would still be necessary for installation.
During their intervention, Eye Security faced challenges after their update was flagged as malware by several security programs, which led to its blockage while leaving the vulnerable updater active. The extent of the risk remains uncertain, but it was reported that they distributed over 2 million update downloads by March, before ceasing further updates and transferring the domains to the Shadowserver Foundation, a non-profit focusing on web security.
Editor’s Take
This development is significant as it underscores the risks associated with outdated software, particularly in apps known for piracy. Users must be vigilant regarding the security threats that can arise from neglected programs. For developers and businesses, it highlights the importance of ongoing support and updates to protect users from potential vulnerabilities.
Source: www.theverge.com